ISO/IEC 27001:2022
Information security management system.
Certificate SI-MC 1755.
Standard as stated: SR ISO/IEC 27001:2023 (ISO/IEC 27001:2022).
Security details depend on the service and environment. Understand what CloudHero needs to access, how changes are controlled and where data is processed before an engagement begins.
The certificates below name MONDO IT GLOBAL SERVICES S.R.L., the legal entity behind CloudHero. Issued by Management Certification on , each states: “Valid until the next annual visa dated: 22.06.2027”.
Custom software development activities (customer-oriented software); information technology and computing management consultancy activities; other information technology service activities; engineering and related technical consultancy activities.
Information security management system.
Certificate SI-MC 1755.
Standard as stated: SR ISO/IEC 27001:2023 (ISO/IEC 27001:2022).
Quality management system.
Certificate C-MC 8606.
Standard as stated: SR EN ISO 9001:2015 (ISO 9001:2015).
Environmental management system.
Certificate M-MC 6844.
Standard as stated: SR EN ISO 14001:2015 (ISO 14001:2015).
These certificates concern the named organization’s management systems within the stated scope. They do not certify individual customer environments or every CloudHero product.
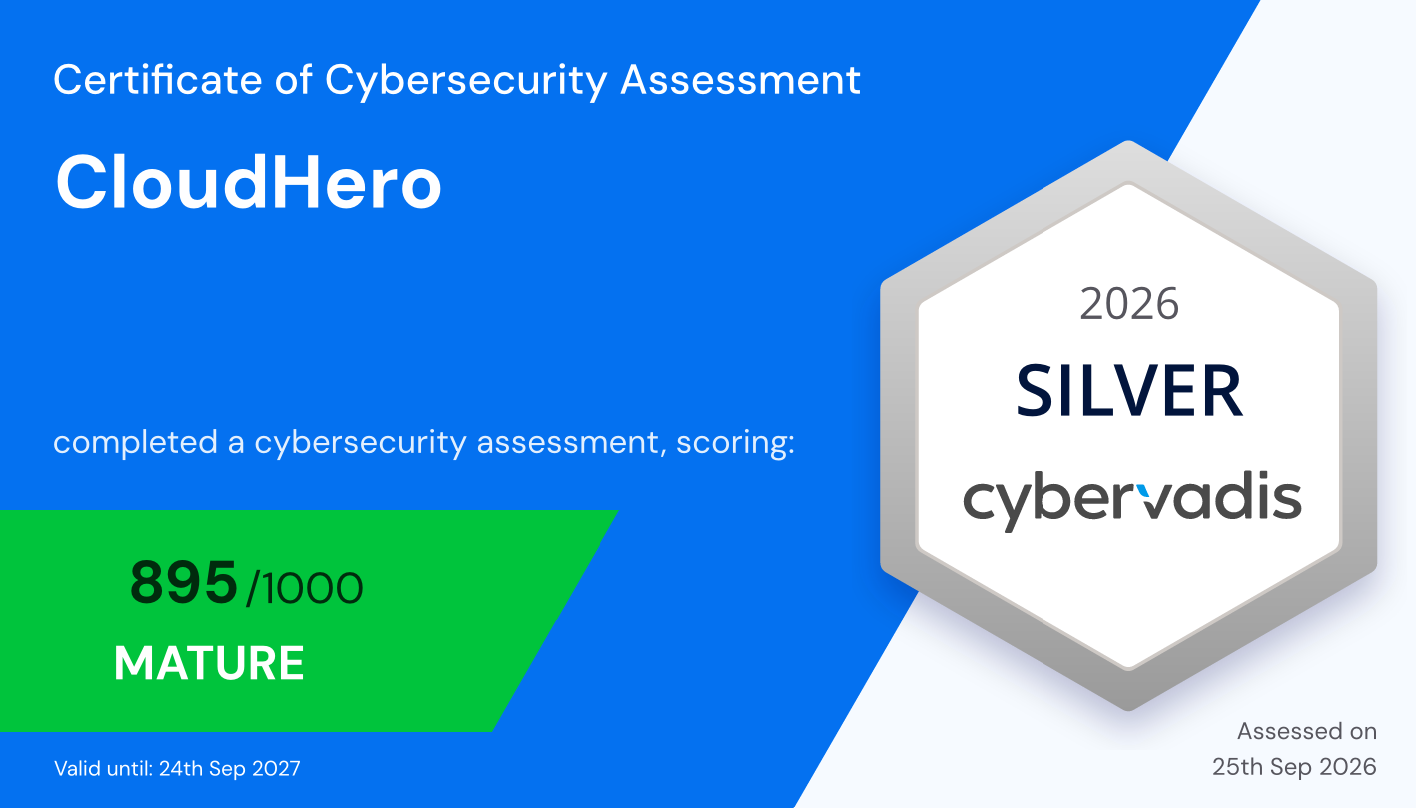
CloudHero completed the CyberVadis cybersecurity assessment on , scoring 895/1000 and receiving a Mature rating and a 2026 Silver badge. The assessment certificate is valid until .
CyberVadis is presented separately from our ISO management-system certifications.
During onboarding, define the covered systems, authorized access, incident channels and production-change approvals. AI-assisted operations also needs an agreed description of the models, data and logging used for your environment.
Request the relevant security documentation and contractual schedule before granting access. Certification details should be read in the context of the named legal entity and the certificate’s scope.
You run the scanner with AWS credentials you control. It collects selected resource metadata, utilization metrics and cost information, then encrypts the collected payload before upload.
CloudHero decrypts the payload in the reporting environment to generate the assessment. Encryption before upload does not mean the data is never decrypted for processing.
What the scanner collects and what its credentials permit are separate questions. A broad AWS-managed read-only policy can allow access beyond the scanner’s collection needs. Review the current policy and instructions with your security team.
The assessment is configured with a 90-day S3 lifecycle for encrypted input and report files. The emailed report link is valid for seven days. For earlier deletion or a complete description of processing providers, logging and retention, contact us before submitting data.
Octora and HeyLeave have their own workflows and data requirements. Obtain their current security and data-processing documentation through the relevant product team. A statement about one product or service should not be assumed to cover all CloudHero work.